AI on your terms.
Managed cloud or self-hosted in your own infrastructure. Bring your own model keys. Audit logs. Custom domains. SAML SSO and SCIM provisioning. Everything you need to roll out AI without surrendering control.
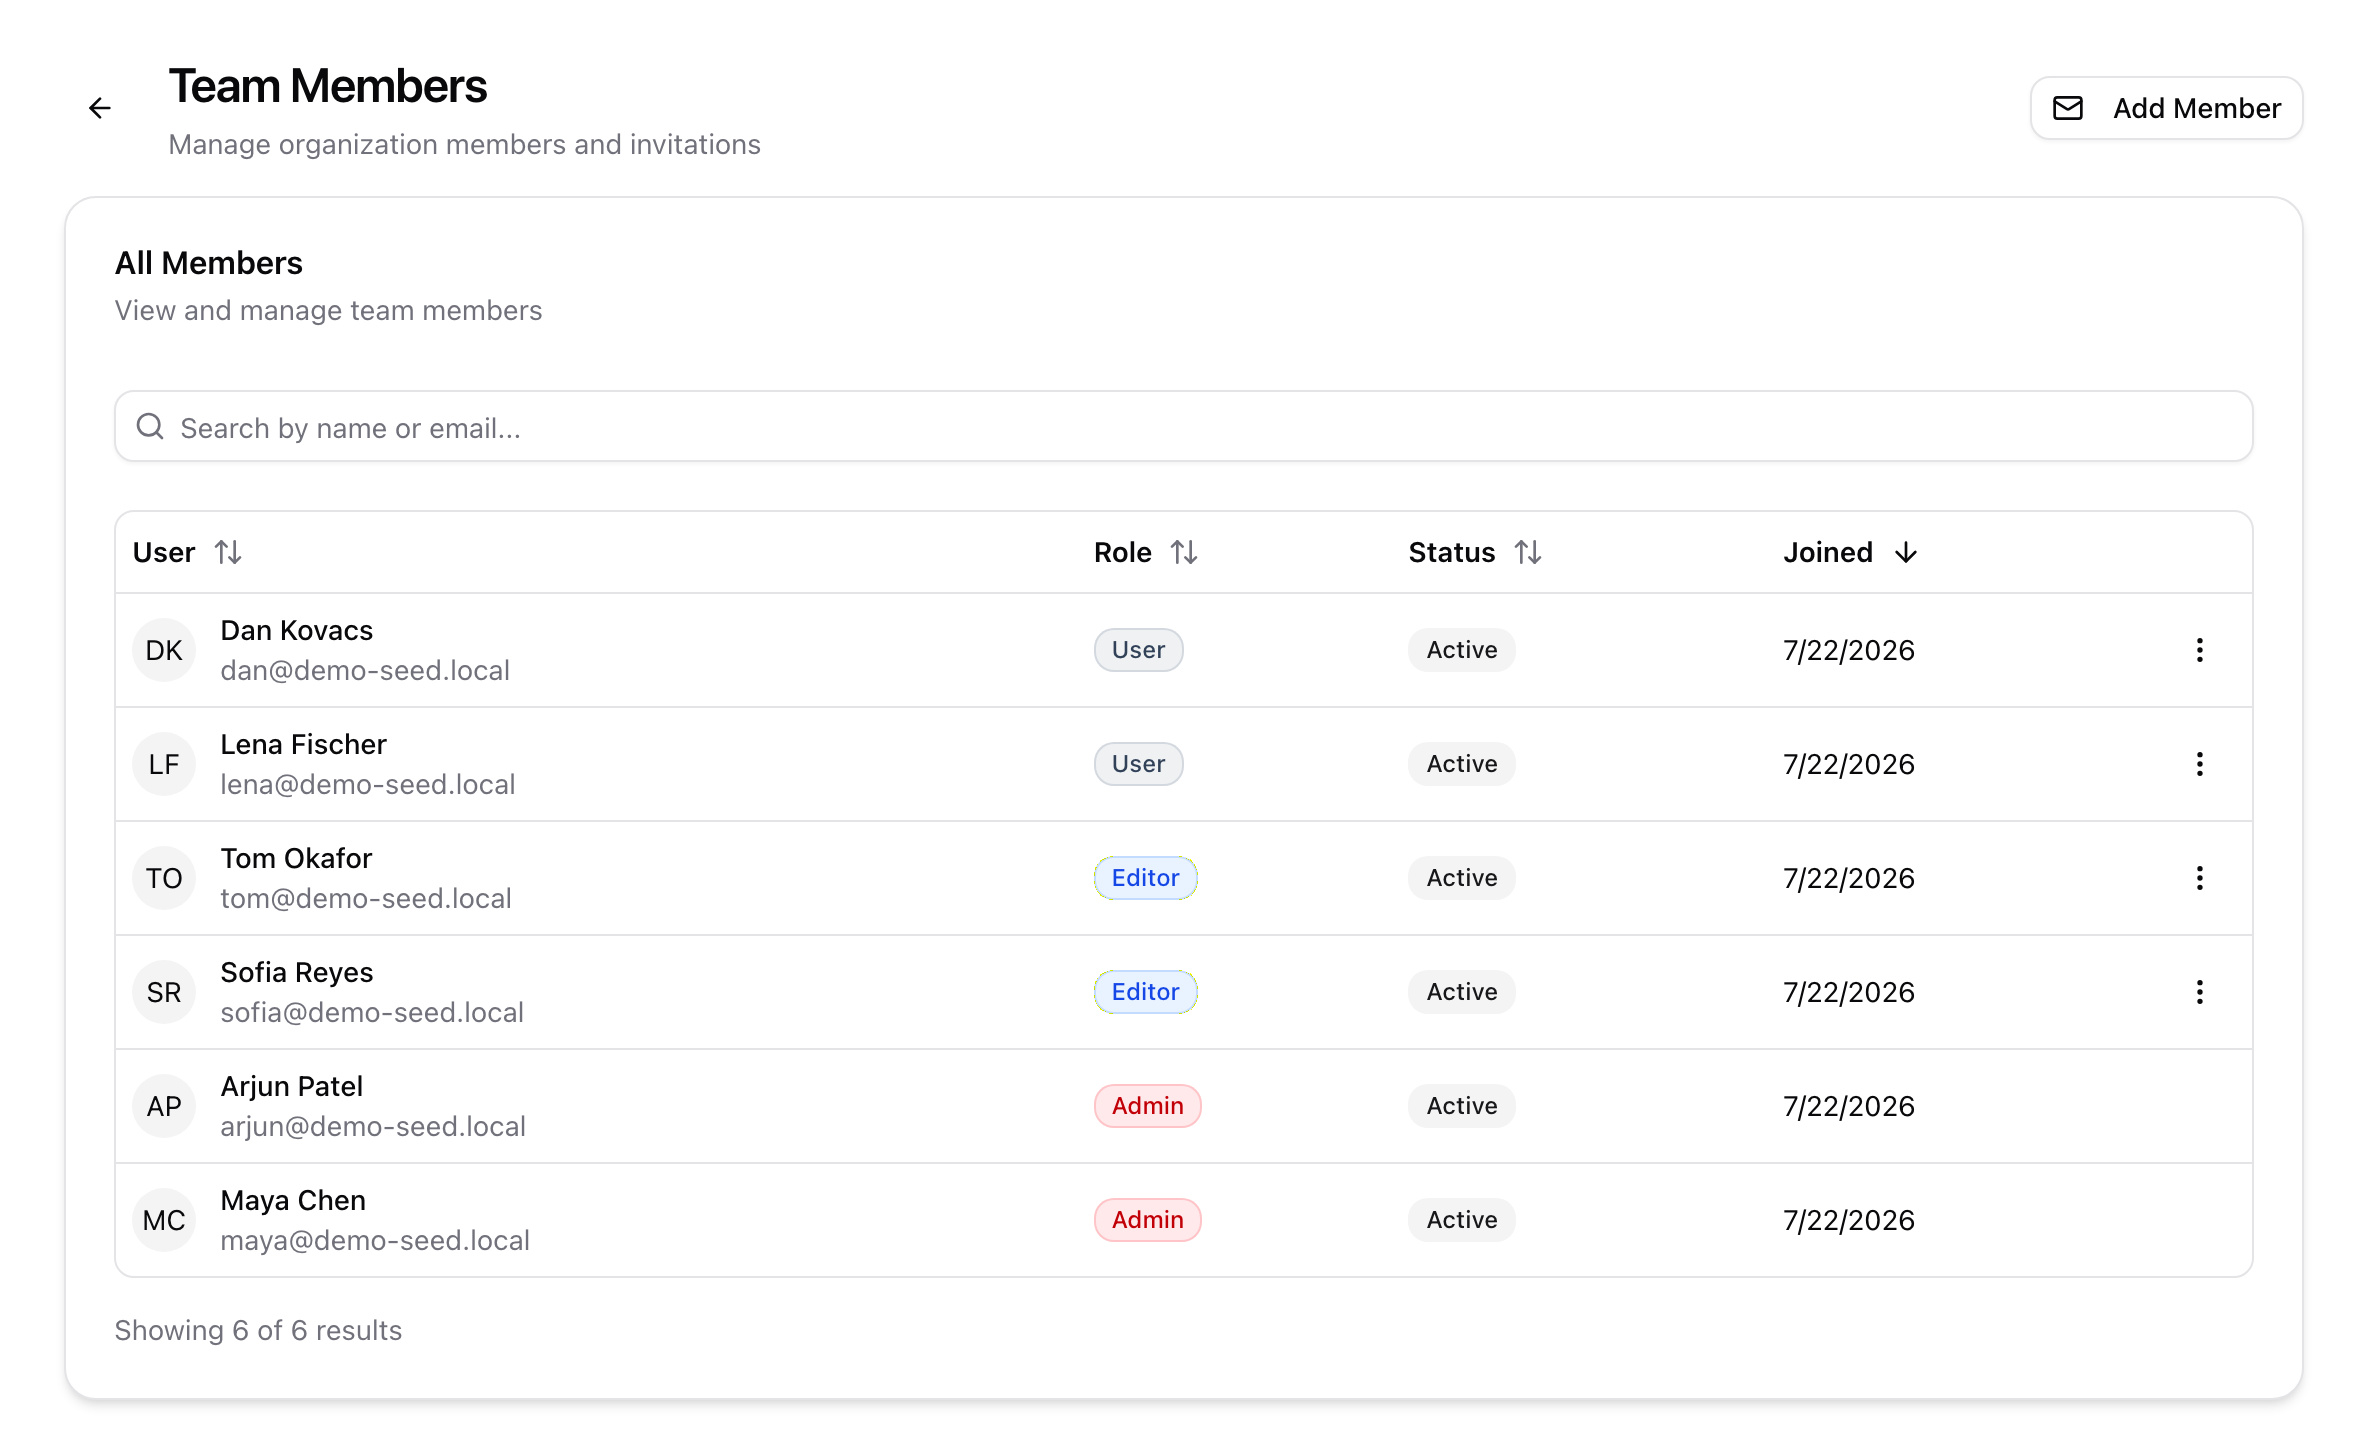
Compliance, scale, and control.
BYOK
Your model keys
Pay model providers directly, with no markup.
SCIM 2.0
Provisioning
Plus SAML and OIDC SSO.
AES-256
Key encryption
Provider keys encrypted at rest.
CSV+JSON
Audit log export
Append-only, per organization.
Managed cloud or your own infrastructure.
Wirebase runs as a managed cloud service on every plan, with every organization isolated at the database row level. On the Enterprise plan it can also be deployed self-hosted in your own infrastructure, on request. You bring your own model API keys, stored per organization and encrypted at rest, so usage is billed to your own provider accounts with no markup. Admins choose which providers and models the organization can use, and can add an Ollama server or any OpenAI-compatible endpoint you run for self-hosted models.
- Managed cloud, every organization isolated
- Self-hosted in your infrastructure (Enterprise, on request)
- Bring your own model keys — no markup on usage
- Admins choose which models the org can use
- Ollama and OpenAI-compatible custom endpoints
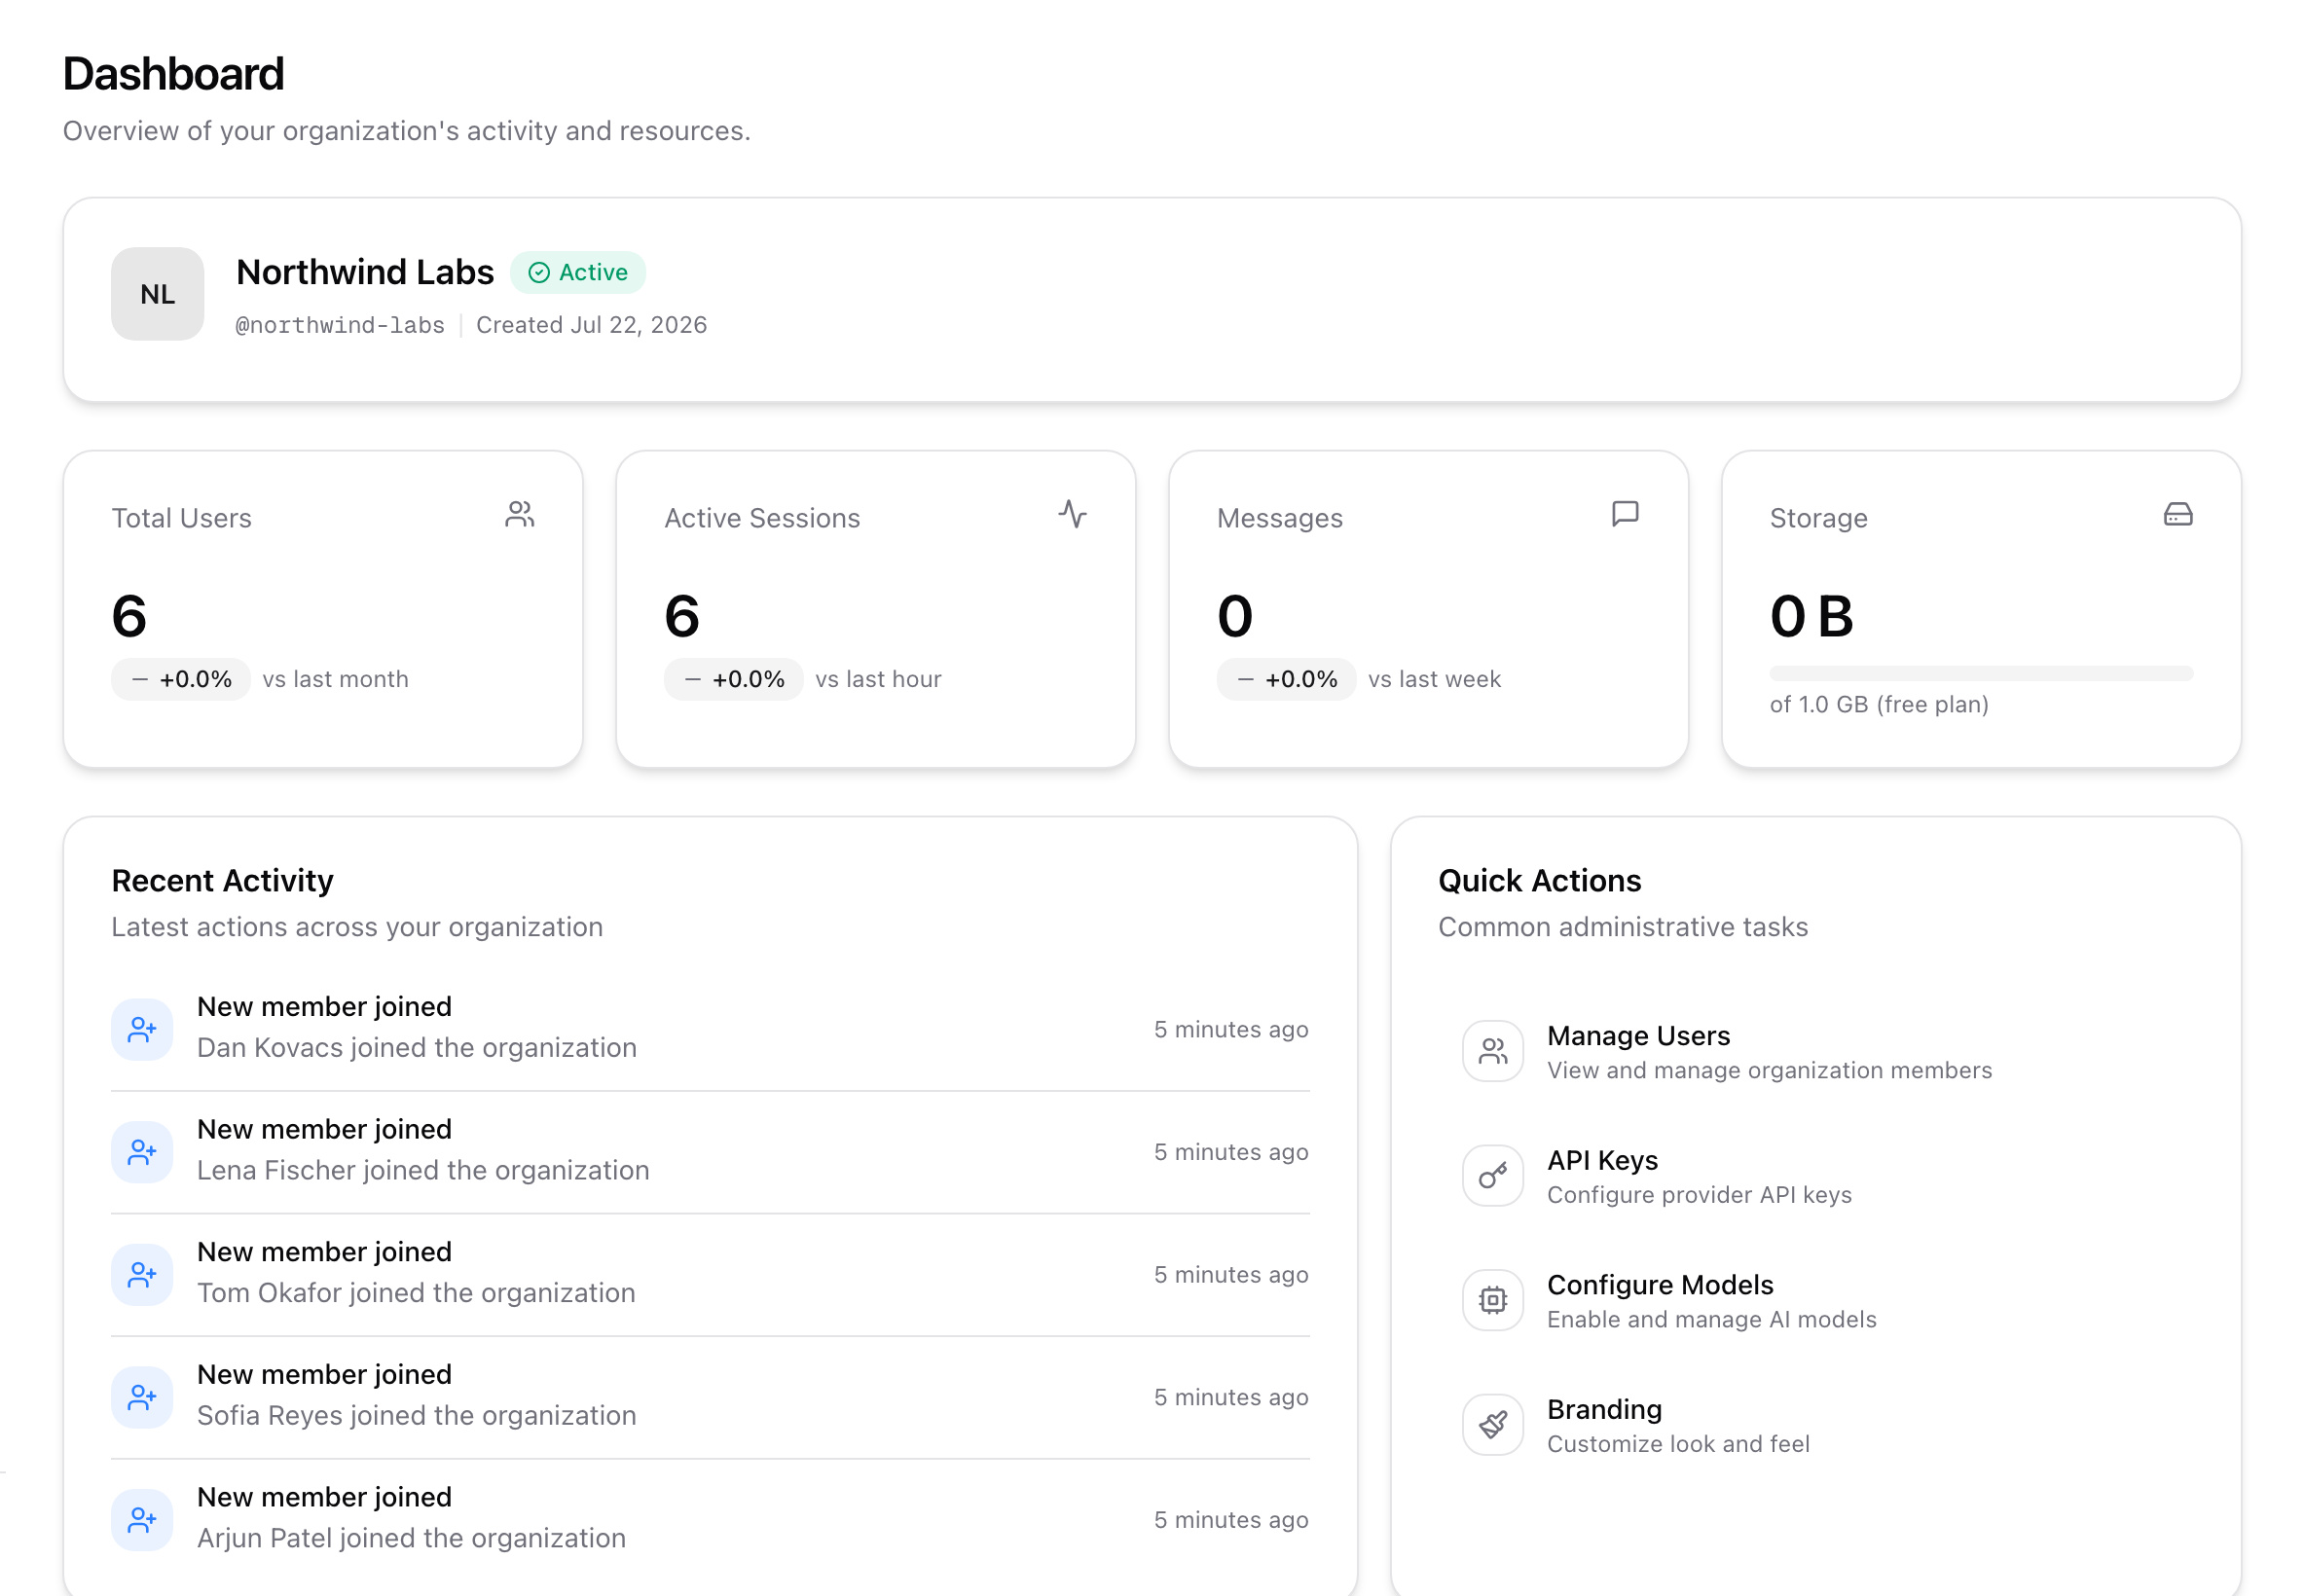
Fits your IdP.
Role-based access control, OAuth sign-in, SAML/OIDC SSO, and SCIM 2.0 provisioning are all available today — new hires get the right access from your IdP, and offboarding is automatic.
- Role-based access (admin, editor, user)
- Per-team subgroups
- OAuth sign-in (Google, GitHub, Microsoft)
- SAML/OIDC SSO and SCIM 2.0 provisioning
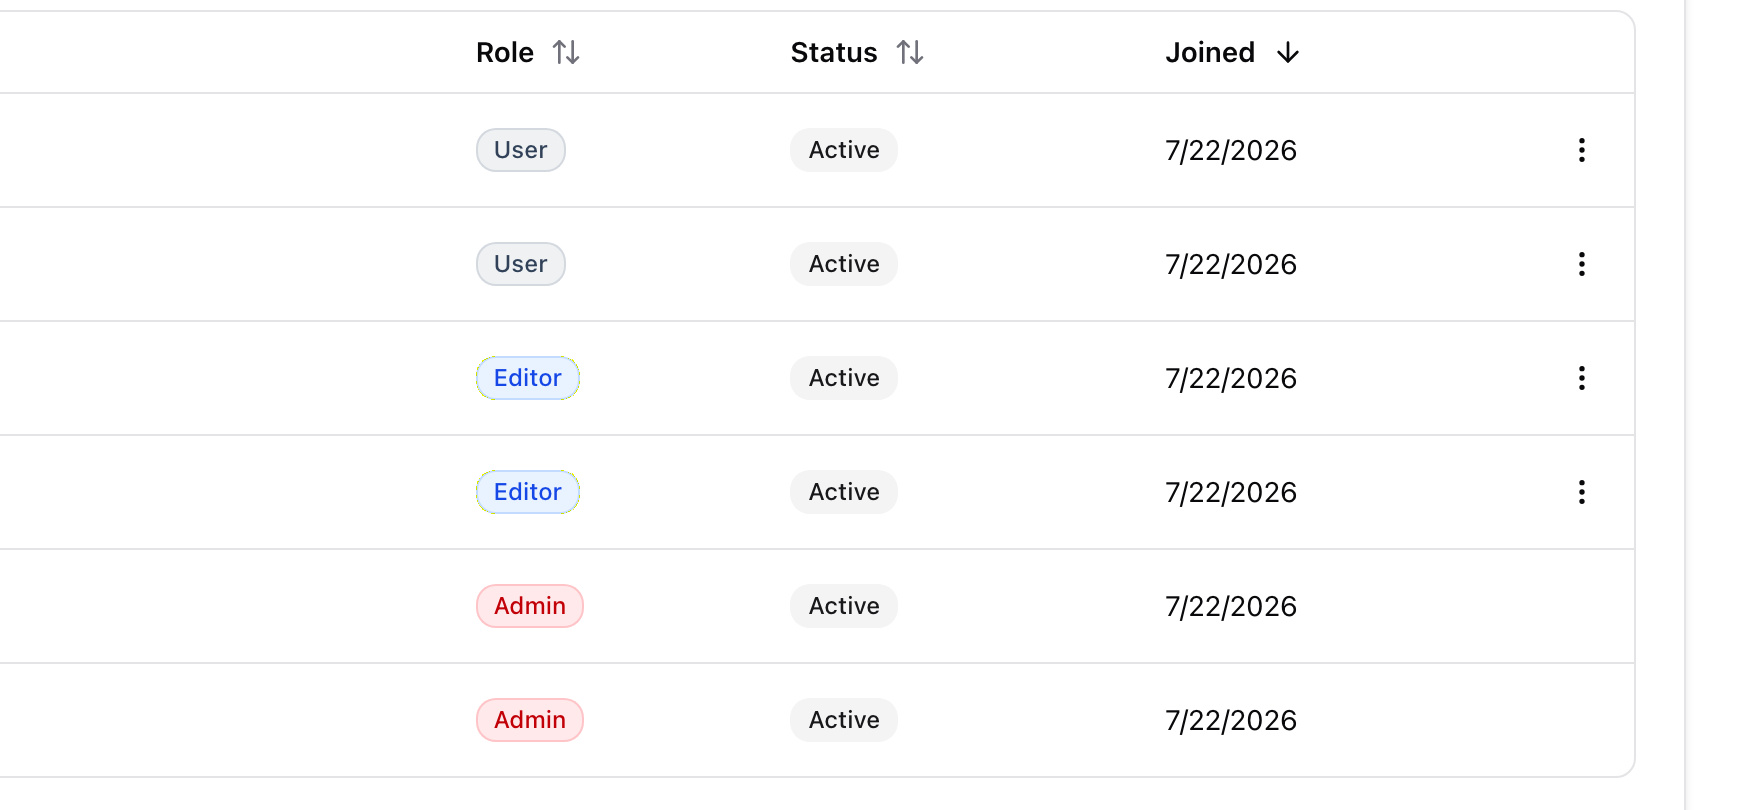
Receipts for every change.
Agent, workflow, connector, and admin changes are written to an append-only audit log that exports as CSV or JSON for your compliance team. Usage is metered per member and per model in admin analytics, and separate monthly spend quotas — set for the organization, a user, or a role — either warn or hard-block once the budget is hit. Provider API keys are encrypted at rest, and organization isolation is enforced at the database row level and verified in automated tests. IP allowlisting for admin access is on the enterprise roadmap.
- Append-only audit log, exportable as CSV or JSON
- Per-member, per-model metering; org and user spend quotas
- Provider keys encrypted at rest (AES-256-GCM)
- Per-org isolation enforced at the database layer
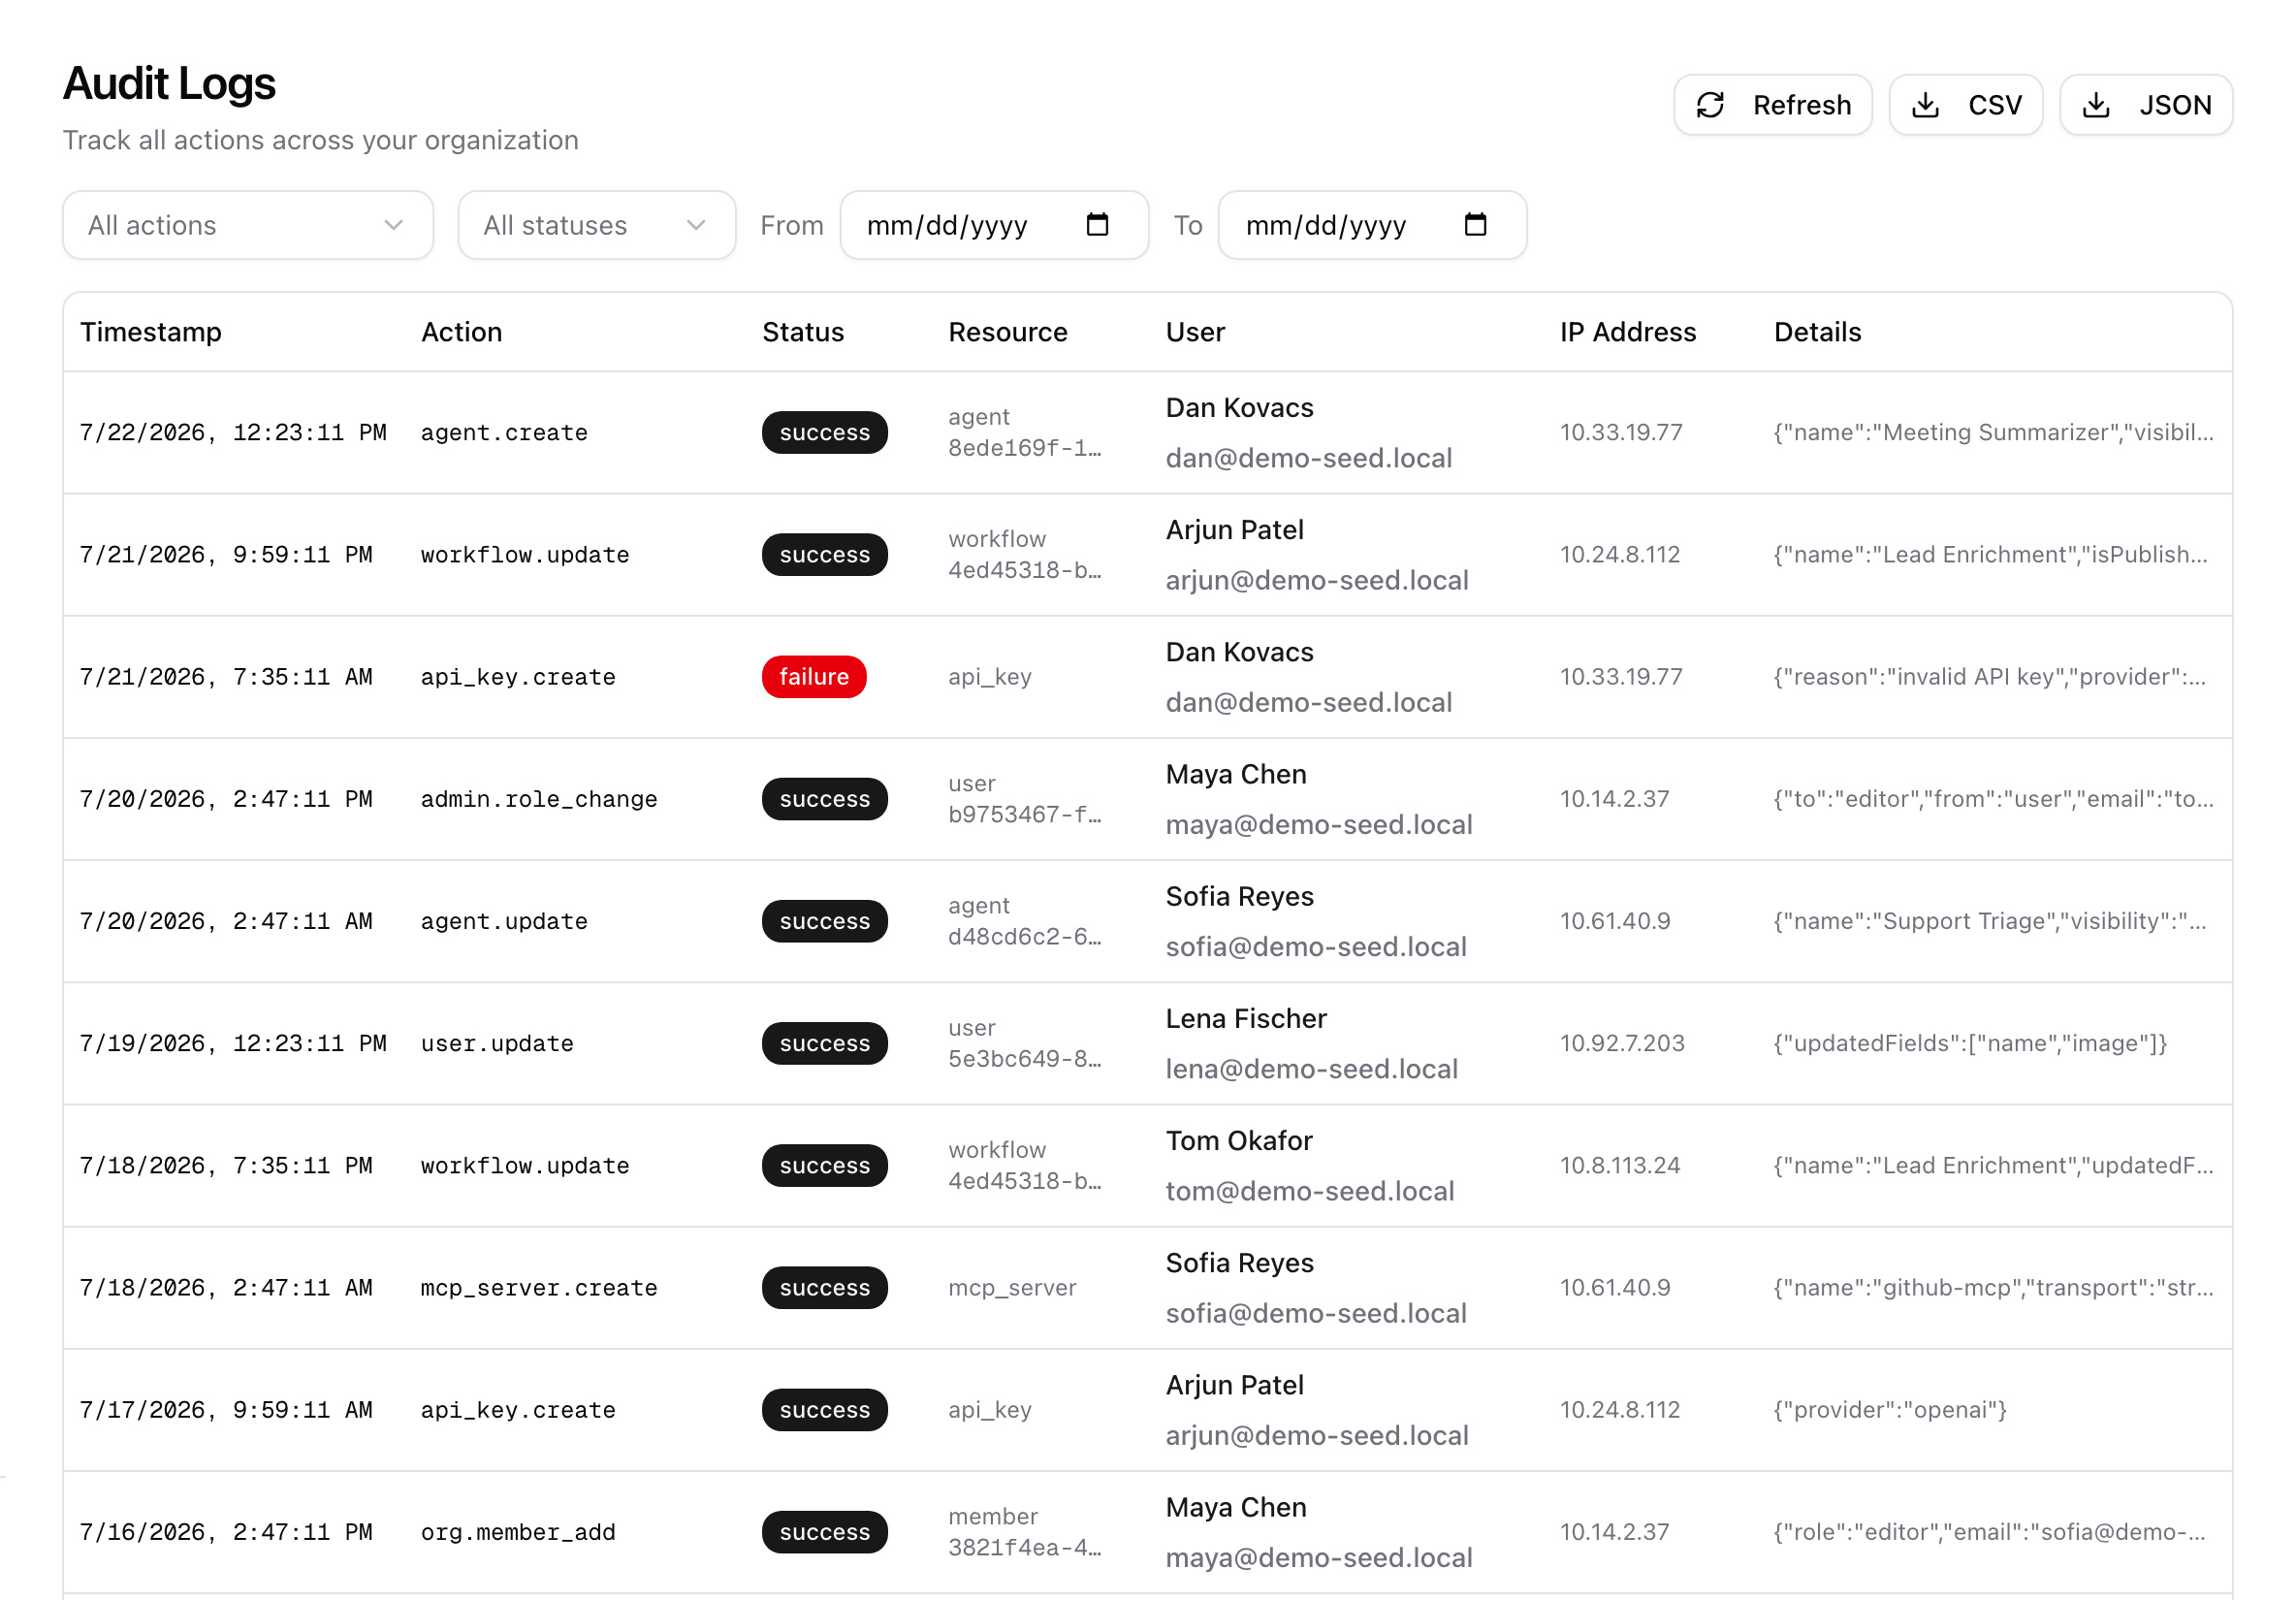
Read the full security architecture, current controls, and roadmap items.
Defensible AI at scale.
Bring your own keys
Provider keys stored per organization, encrypted at rest.
Identity
SAML SSO and SCIM provisioning for enterprise IdPs.
Audit logs
Append-only, exportable per organization.
Usage governance
Per-org quotas, budgets, and analytics.
Custom domain
Your brand, your URL.
White-label
Your logo, colors, and domain.